Services

Purpose-Built Security
for Regulated Organizations

Structured, practitioner-led services designed to build defensible security programs aligned to HIPAA, HITRUST, and proven security methodologies — with auditor-ready evidence at every stage.

20+

YEARS OF PRACTICE

4

CORE SERVICE LINES

18

CONTROL DOMAIN

SCORED

100%

AUDIT-READY OUTPUT

Risk Management

Identify, assess, and prioritize risks with actionable strategies to strengthen your security posture.

Security Advisory

Get expert security leadership and guidance when you need it, from strategic planning to ongoing support.

Managed Services

Reduce cyber risk with ongoing security management, monitoring, and compliance support.

Penetration Test

Identify exploitable vulnerabilities before attackers can use them against your organization.

What we do

Four core service lines. One defensible program.

Each engagement is scoped to your regulatory environment, operational maturity, and the service mix that fits your organization.

Padlock shield representing regulatory compliance

RISK ASSESSMENT

Risk Management

The Cyber Security Resource assessment methodology allows for executive reporting outputs and actionable next steps that ensures you find the business partner you are after.

Hand holding a tablet with a global network overlay

ADVISORY.VCISO

Security Advisory

Whether you are looking for an interim CISO, an IT security resource to support your CISO or a longer-term vCISO advisor, our Virtual CISO Advisory Services provide the leadership you need, when you need it.

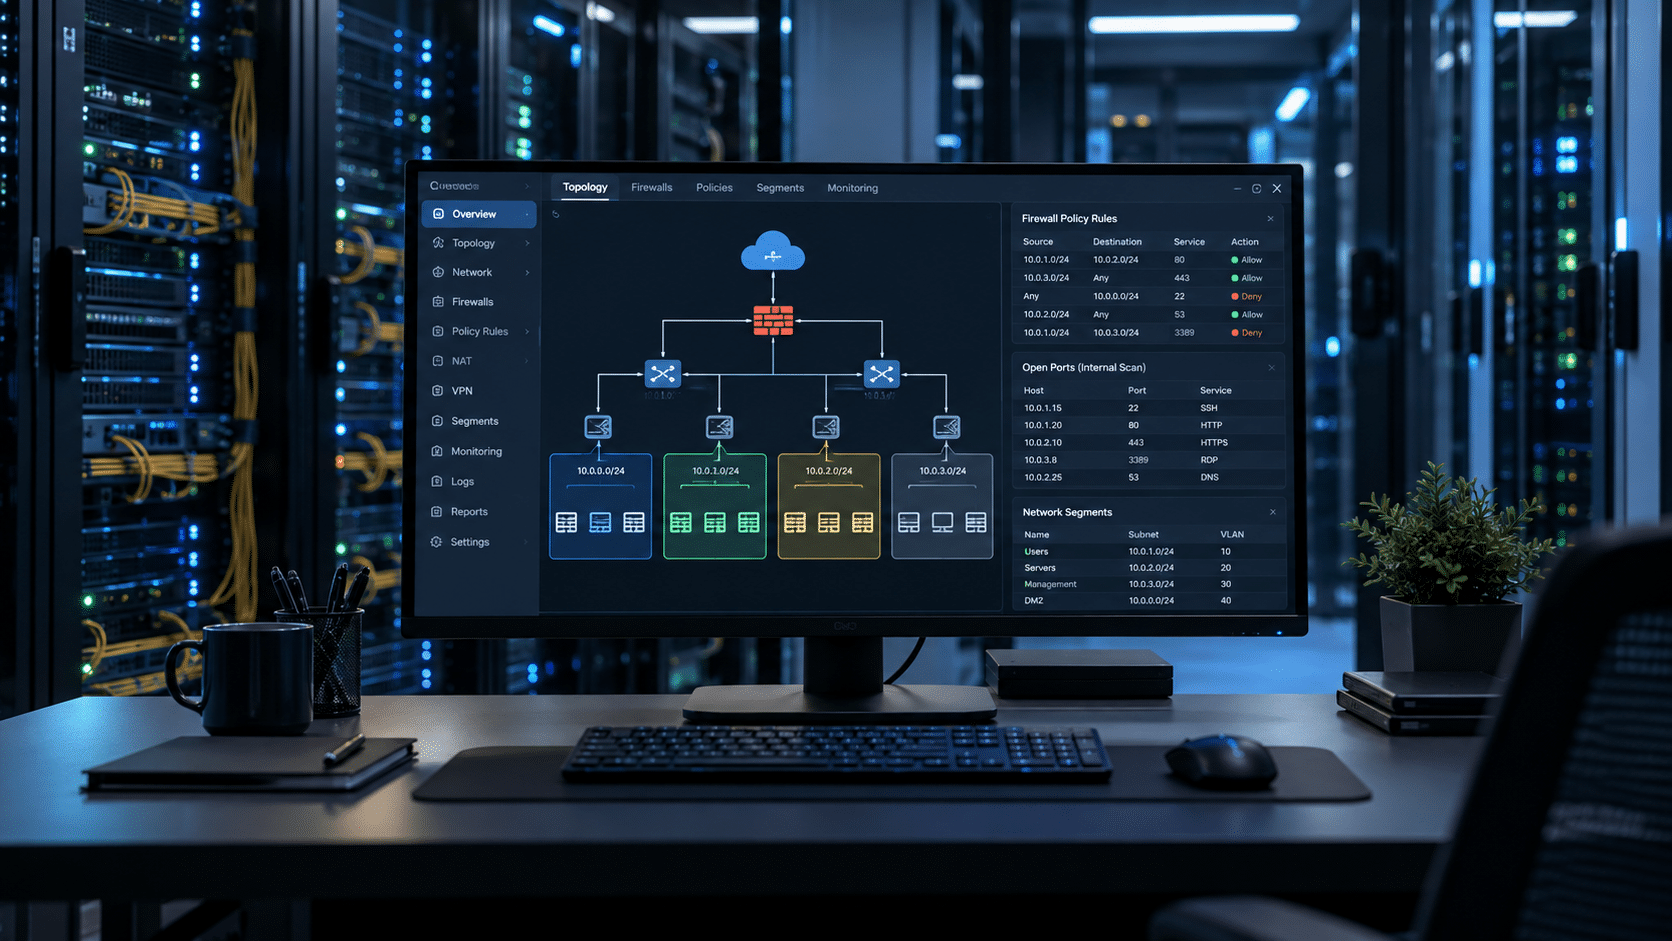
Security operations center monitors

MANAGED.TPRM

Managed Services

We offer third-party risk management (TPRM) services that mitigate risk by assessing relationships, business profiles, and cyber risk through customizable workflow automation and industry-specific compliance standards.

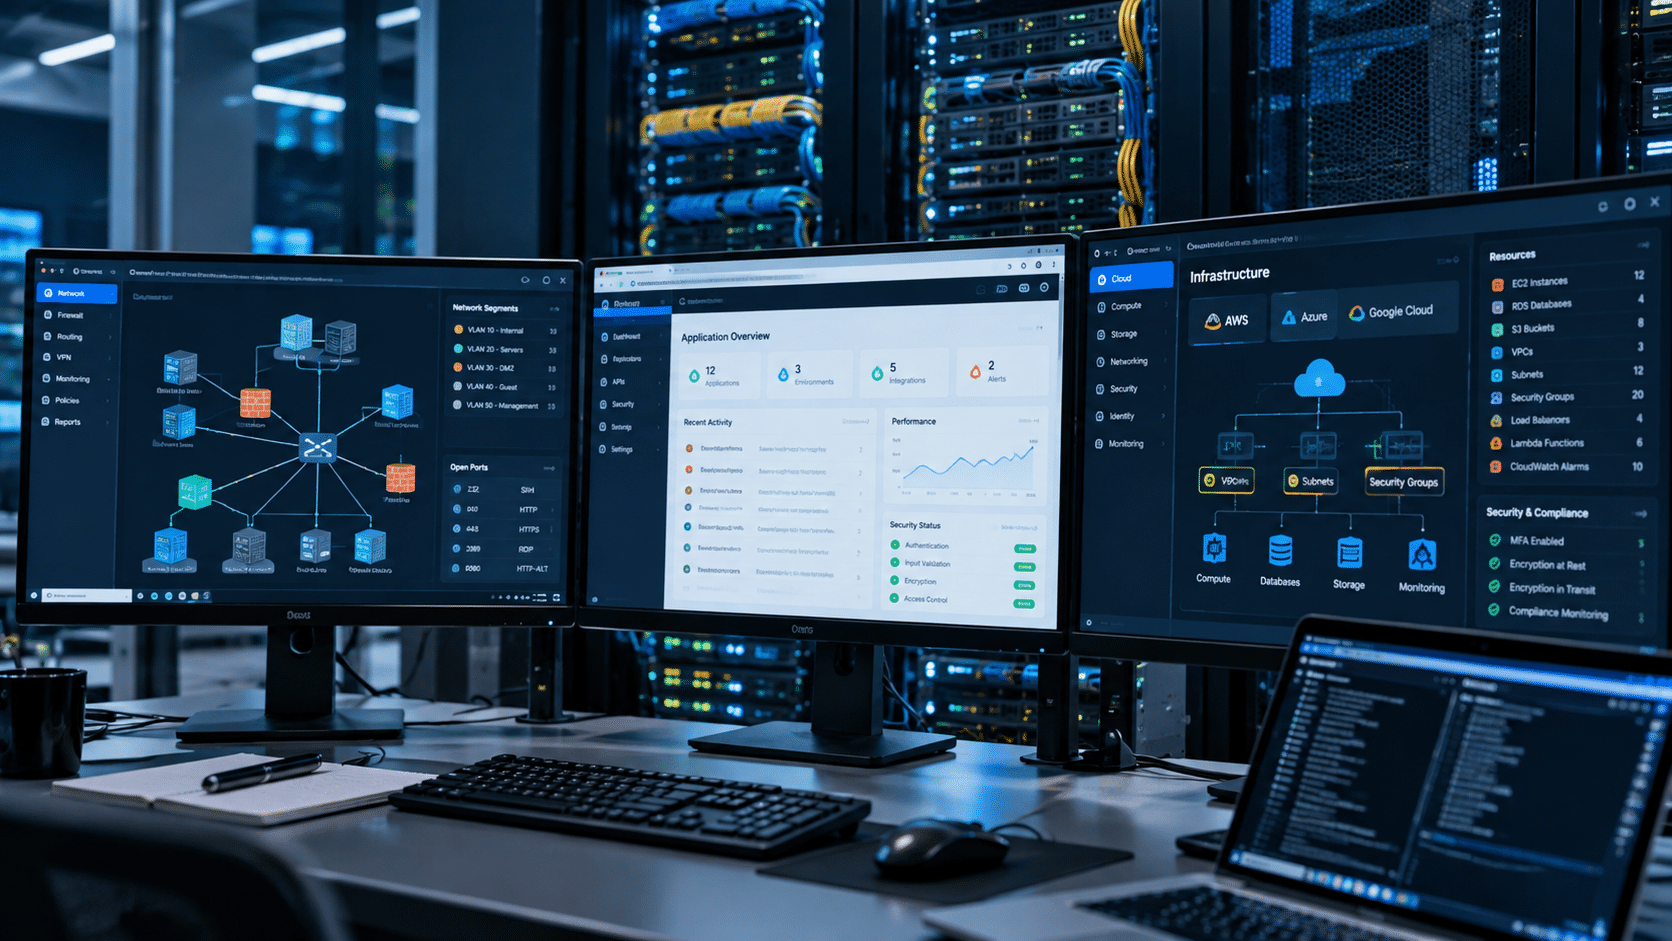
Security analyst workstation with multiple monitors

PENTEST.NETWORK

Penetration Test

Our Penetration Testing Services simulate real-world attacks against your network, web applications, and cloud environments to identify exploitable vulnerabilities before they impact your organization, customers, or compliance posture.
MANAGED SERVICES

Continuous oversight without expanding headcount

Each managed service is delivered as a standalone engagement with clear scope, reporting, and accountability.

Abstract data concept with digital network lines

VULNERABILITY MANAGEMENT

Continuous scanning, structured analysis, risk-based prioritization, and remediation tracking for regulated environments.

Businessman holding a glowing globe

THIRD-PARTY RISK MANAGEMENT

Vendor onboarding assessments, ongoing monitoring, risk register management, and audit-ready documentation.

Cybersecurity operations desk with dashboards

ENDPOINT DETECTION AND RESPONSE

Continuous endpoint monitoring, threat detection, rapid containment, and incident response support.

PENETRATION TESTING

Validate exposure before attackers do.

Manual, methodology-driven testing aligned to OWASP Top 10 and industry best practices.

Programming code on a screen

pentest.network

Network Penetration Test

External, internal, and cloud infrastructure testing with manual exploit validation and risk-prioritized reporting.

Green binary code streaming on a screen

pentest.webapp

Web Application Penetration Test

OWASP Top 10 aligned testing for authentication, authorization, injection, API, and session security flaws.

Earth at night from space showing connected cities

pentest.CLOUD

Cloud Security Test

Configuration review, access control validation, and exposure analysis for AWS, Azure, and hybrid cloud environments.

Get Started

Build a Security Program

You Can Defend

Schedule an intro call with a seasoned practitioner. We will review your security priorities and map a practical path forward.

Scroll to Top